BOOK NOW FREE LIMOUSINE BUS
Discount to 49% of for Early Bird Promotion

BOOK NOW FREE LIMOUSINE BUS
Discount to 49% of for Early Bird Promotion

BOOK NOW FREE LIMOUSINE BUS
Discount to 49% of for Early Bird Promotion

BOOK NOW FREE LIMOSINE BUS
Discount to 49% of for Early Bird Promotion
BOOK NOW FREE LIMOSINE BUS
Discount to 49% of for Early Bird Promotion
BOOK NOW FREE LIMOSINE BUS
Discount to 49% of for Early Bird Promotion
A New Perspective at Casino Security Measures
10:54 am | September 4, 2026

When someone visits an online casino as a newcomer, the glitter of slot animations and the promise of a welcome bonus often draw immediate attention. Beneath that exterior, however, runs a sophisticated network of protocols that determine whether a platform earns trust. Modern casino security is not simply a simple matter of a padlock icon in the browser bar; it encompasses encryption standards, identity verification rituals, payment gateway hardening, game fairness certification, and behavioural monitoring systems that function silently in the background. Comprehending these layers transforms a player from a hopeful gambler into an informed consumer who can spot genuine protection versus cosmetic assurances. This article examines the protective architecture that supports a well-built gaming environment and details what practical questions to ask before depositing real money.
The way Encryption Secures Every Data Exchange
The initial line of defence in any online casino is the encryption protocol that wraps every interaction between a player’s device and the platform’s servers. Transport Layer Security (TLS), the successor to SSL, establishes an encrypted tunnel that scrambles login credentials, payment card details, and personal identification data into ciphertext unreadable to any third party intercepting the traffic. Modern implementations depend on TLS 1.2 or 1.3, with the latter offering faster handshakes and discarding obsolete cryptographic algorithms that earlier versions supported. Visitors can confirm this by inspecting the browser address bar: a valid certificate issued by a trusted Certificate Authority confirms the connection is encrypted, and clicking the padlock displays details about the issuing entity and the encryption strength, typically 256-bit AES keys for symmetric encryption alongside elliptic curve Diffie-Hellman key exchange.
Beyond the transport layer, reputable casinos apply encryption at rest to data stored on their servers. Customer databases, transaction records, and identity documents sit behind Advanced Encryption Standard (AES) protection so that even if physical drives were compromised, the information would remain inaccessible without the decryption keys. Key management practices play a role here: hardware security modules (HSMs) generate and store cryptographic keys in tamper-resistant appliances, ensuring no single administrator can extract the master keys manually. Players should know that encryption is not a one-time checkbox but an ongoing lifecycle of certificate renewal, vulnerability patching, and cryptographic agility that allows swift replacement of weakened algorithms if the security community deprecates a standard. The practical takeaway is verifying the padlock and ensuring the certificate belongs to the actual domain, not a lookalike, before typing any sensitive information.
Incident Response and What Players Should Monitor
No security system stops all breaches, making response capability the distinguishing factor between a minor disruption and a major security failure. Experienced providers maintain an cyberattack playbook that defines monitoring approaches (intrusion detection systems, SIEM alert correlation), containment procedures (segment isolation, forced password resets across affected cohorts), digital evidence procedures, and legal reporting deadlines. Many gaming authorities require reporting within three days of verifying a security incident involving personal or financial data, and the official statement should clarify what details were leaked, what actions the provider has implemented, and what steps impacted users must take—typically password changes, MFA review, and monitoring of financial statements for suspicious activity.
Players can watch for secondary clues of an provider’s security practices. A specific reporting method or bug bounty program indicates the company accepts security findings from outside experts rather than considering them hostile. Historical data compromise reports, findable through incident tracking platforms, shows if the company experienced previous breaches and how openly it managed them. An additional method is how the support team handles a security-related question: checking if the site enables FIDO2/WebAuthn security keys or asking about the SSL certificate provider should produce detailed technical responses, not prepared avoidance. The missing standard security headers—Content-Security-Policy, Strict-Transport-Security, X-Content-Type-Options—can be checked through browser developer tools and signals whether security engineering teams actively configure the web server layer. Players who understand these indicators move beyond blind trust and make evidence-based decisions about where to invest their finances and privacy.
Licence and Oversight Oversight as a Trust Foundation
A casino’s security framework begins with the regulatory body that issues its gaming licence, because regulators mandate mandatory technical and procedural criteria before licensing and conduct routine inspections afterwards. Well-known regulatory authorities such as the Malta Gaming Authority, the UK Gambling Commission, the Kahnawake Gaming Commission, or the Curacao eGaming authority each apply rules covering player fund isolation, anti-money laundering measures, and technical system assessments. The licence number must appear openly, usually in a page footer, and players can cross-reference it against the regulator’s online record to verify the operator remains in good repute. This step should never be overlooked: an unverified licence statement is a red flag regardless of how refined a website looks.
Regulatory oversight goes into dispute resolution mechanisms. Licensed operators must provide a complaints process and, if the player remains unhappy, an escalation route to an independent alternative dispute resolution (ADR) provider like eCOGRA or ThePOGG. These entities assess material from both parties and deliver binding or non-binding determinations according to the licence provisions. The mere existence of this process influences operator behaviour, because outstanding disputes that are escalated to the regulator can result in sanctions, licence withdrawal, or cancellation. Furthermore, many regulators mandate that player funds be maintained in segregated accounts, legally isolated from operating capital, so that even in an insolvency scenario customer balances remain protected and returnable. Before signing up, a player should identify the licence seal, access the regulator’s website, type the listed licence number, and check it aligns with the operator name and website address.
Account-based Safeguards and Entry Control
An account containing a balance is a goal, and the security industry has agreed on a layered model that integrates mandatory measures with optional tools players should enable. Multi-factor authentication (MFA) serves as the single most efficient account protection a player can activate, typically through a time-based one-time password (TOTP) produced by an authenticator app like Google Authenticator or Authy. SMS-based codes offer weaker protection due to SIM-swapping vulnerabilities, so app-based or hardware key methods are better. Once MFA is activated, even a fully compromised password cannot give an attacker account access without the second factor. Players should confirm whether the casino supports MFA and, if it does, turn on it immediately after registration.
Session management controls form the next ring. Casinos should automatically end idle sessions after a configurable timeout, record all active sessions with visible details (device type, IP address, browser, login timestamp), and provide a one-click facility to remotely log out other sessions. This enables a player who accidentally left an account open on a shared or public device to terminate that session from anywhere. IP and geolocation anomaly checks trigger silent alerts or temporary restrictions when a login attempt comes from a country or city far removed from the player’s established pattern, especially when the time between logins makes physical travel impossible. Additional protective features some platforms include are withdrawal lock timers where the player configures a mandatory cooling-off period before any withdrawal request goes through, giving the true account holder time to identify and reverse an unauthorized request. Responsible gambling tools—deposit limits, loss limits, session time reminders—also function as security instruments by capping the damage an account takeover can inflict in a short period.
Identity Verification for Players and How It Works in Practice
Customer identification processes often annoy players who expect instant withdrawals after a lucky session, but they fulfill a security purpose that goes beyond regulatory compliance. Identity verification stops account takeovers by confirming that the person submitting a withdrawal corresponds to the person who originally created an account and deposited. The process typically includes submitting a government-issued photo ID (passport, national ID card, or driver’s licence), a recent utility bill or bank statement indicating the registered address, and occasionally a photograph of the physical payment card with only the last four digits visible and the CVV covered. Automated systems review these documents for tampering, match facial biometrics from the ID photo against a live selfie taken during submission, and cross-check names against international sanctions and politically exposed persons lists.
The timeline varies by operator and by how clearly the player submits documents. Automated verification can complete in under five minutes when scans are high-resolution, free of glare, and fully show all four corners of the document. Manual review, triggered by mismatches or flagged risk indicators, stretches to 24–48 hours. Players should organize materials in advance: photograph documents flat on a dark background using natural light, avoid cropping edges, and ensure the name and address exactly correspond to the registration details. A mismatch between a registered street abbreviation and the full word on a bill can delay the process unnecessarily. The security benefit for the community is that thorough KYC makes it exponentially harder for fraudsters to wash money through casino accounts or to execute account takeover attacks using stolen credentials purchased from dark web markets.
Information Privacy and Accountable Information Handling
Security and confidentiality coincide substantially, yet they deal with various dangers: protection defends against unauthorized access, while privacy governs what the provider carries out with records it lawfully maintains. The General Data Protection Regulation (GDPR) in Europe and equivalent systems in other regions define guidelines that any casino serving worldwide audiences should adhere to, such as data minimization (collecting only what is necessary), purpose constraint (not reassigning KYC documents for irrelevant marketing analytics), and archiving restriction (deleting data after the prescribed holding period lapses). The privacy policy section should clearly enumerate every category of data gathered, the statutory foundation for processing each class, and the third-party processors engaged—payment processors, identity validation services, CRM systems, and analytics providers.
Customers have actionable rights under sound privacy regulations: the right to view all data kept about them, the right to correction of inaccuracies, the entitlement to removal once the operational engagement ends and required retention durations lapse, and the ability to data portability in a machine-readable format. Exercising these entitlements also acts as an casual security check: if a subject access inquiry returns messily arranged data containing other users’ data, the operator’s inside measures are hazardously lacking. Cookie consent systems, while occasionally an nuisance, should offer precise control over marketing and analytics cookies and must not bundle permission as a condition of entering the system itself. A privacy-respecting gaming platform separates marketing communication choices from essential service communications, permits cookie preference modifications at any time, and never sells or leases customer records to third parties without clear, distinct opt-in consent.
Fairness Audits and RNG Certification
Security is embedded in the games themselves through mathematical audits that validate slot returns, table game shuffles, and random number generator (RNG) operation. Independent testing laboratories such as iTech Labs, GLI (Gaming Laboratories International), and BMM Testlabs examine the source code of RNG implementations to ensure they produce statistically comparable outputs from true randomness across millions of simulated rounds. They evaluate biases, periodicity (repeating sequences), and vulnerability to prediction, and they certify that the published Return to Player (RTP) percentages correspond to the actual mathematical model. Certification reports often appear as clickable badges within game lobbies or in an easily accessible fairness page, and players can check certificate numbers on the testing lab’s public database.
Live casino games substitute RNG with physical equipment, moving the fairness burden to procedural controls. Cameras cover every angle of the dealing table and roulette wheel, and pit bosses oversee for irregularities. Shoe changes, deck shuffles, and wheel maintenance follow documented schedules that regulators audit. Optical character recognition captures every card value in real time and cross-references the digital output against the video stream so that any discrepancy triggers an immediate investigation. Players evaluating game fairness should seek two separate indicators: the RNG or game fairness certificate from an accredited lab for virtual games, and a description of the live studio’s regulatory oversight for live dealer products. These certifications are not permanent; labs require periodic re-testing, particularly after game logic updates, so checking certificate dates verifies the audit remains current.
Phone and App Security Factors
Playing on a smartphone introduces platform-specific security aspects that desktop-only assessments miss. A correctly built native casino application distributed through official stores (Apple App Store or Google Play) profits from the store’s own malware scanning, developer identity verification, and sandboxing enforcement that restricts the app’s ability to access unrelated parts of the device. iOS sandboxing, in particular, stops apps from reading data belonging to other apps, and App Transport Security mandates encrypted network connections for all communications. Android’s Google Play Protect scans apps continuously even after installation for behavioural changes suggestive of compromise. Players should refrain from downloading casino APK files directly from websites unless the operator offers a verifiable signature and hash that can be cross-checked after download.
Progressive Web Apps (PWAs) and mobile-responsive browser play sidestep native app requirements, relying instead on the browser’s security model https://greenluckcasino.eu/. Biometric authentication built into modern devices—fingerprint sensors, Face ID, or iris scanners—offers a convenience layer that pairs with the casino’s MFA implementation: the authenticator app can itself require biometric unlock before displaying the TOTP code, creating a sequence where both the phone unlock and the code retrieval require physical user presence. Players should keep up-to-date operating system versions because casino apps and mobile sites depend on the device OS for TLS library updates, root certificate store management, and keyboard security (preventing third-party keyboards from capturing typed passwords). The practical checklist contains installing only from official stores, keeping OS updates current, using biometric locks on both device and authenticator apps, and never jailbreaking or rooting a device used for financial transactions.
Transaction Gateway Safeguards and Transaction Surveillance
Funding into a casino account activates a series of behind-the-scenes checks designed to verify the payment instrument, the user’s authority to use it, and the validity of the transaction itself. Payment gateways compliant with PCI DSS Level 1 standards handle card data handling under strict segmentation rules, ensuring the casino never sees the full primary account number; instead, a tokenized representation travels between systems, making intercepted data useless. Three-Domain Secure protocols (3DS2) add a friction layer where the cardholder’s bank authenticates the transaction via biometric verification, a one-time passcode, or a push notification to the banking app. This protocol shifts liability for fraudulent card-not-present transactions from the merchant to the issuing bank, motivating banks to uphold robust challenge flows.

Beyond card channels, alternative payment methods each bring their own security properties. E-wallets like Skrill and Neteller serve as intermediaries that protect bank account details from the casino entirely, while direct bank transfers often utilize open banking APIs with strong customer authentication required by PSD2 in European jurisdictions. Cryptocurrency deposits, when supported, shift verification to the blockchain: the casino tracks network confirmations and can implement address whitelisting features that limit withdrawals to pre-approved wallet addresses only. Transaction monitoring systems complement these gateway protections by analyzing a player’s deposit patterns and detecting anomalies such as sudden large-value transactions from a previously unused device or location, multiple failed deposit attempts across different cards within a short window, or deposit amounts structurally suggestive of money laundering layering. The monitoring operates continuously, not just at deposit time, and can prevent suspect transactions in milliseconds.
What Users Can Do Today to Strengthen Their Position
Studying security architecture is helpful, but the real value lies in turning knowledge into a personal checklist completed before depositing. Some steps take seconds, others require ongoing habits, but together they significantly reduce exposure to the most common attack vectors and operator shortcomings. The following items constitute a concrete action plan taken from the layers discussed throughout this article. No single measure is sufficient alone, but the combination builds overlapping defences that intercept threats slipping through any one layer.
- Check the licence number against the regulator’s public register and ensure the registered domain matches the site being visited; note the ADR provider’s contact page in case of future disputes.
- Inspect the TLS certificate by clicking the browser padlock and check that it was issued to the exact domain, not a parent holding company domain, and that the validity period has not expired.
- Activate app-based multi-factor authentication immediately after registration and configure the authenticator app with biometric protection on the device itself.
- Browse the testing laboratory’s certificate database for the RNG and fairness certifications claimed on the site, and note the audit date to confirm it is current.
- Read the privacy policy’s third-party processor list and submit a subject access request as a practical test of the operator’s data governance maturity.
- Utilize unique, high-entropy passwords generated by a password manager; never repeat a casino password across other services, because credential stuffing attacks exploit cross-site password reuse.
- Establish deposit and loss limits during the first session, regarding them as security controls that cap potential damage from an undetected account compromise.
- Check the browser developer console’s network tab for the presence of Strict-Transport-Security and Content-Security-Policy headers as quick indicators of web server configuration diligence.
Protection in an online casino is not a product feature listed on a promotional banner; it is a ongoing, multi-vendor effort spanning cryptography, regulatory compliance, identity verification, financial monitoring, mathematical auditing, and privacy engineering. A operator that invests in these layers makes that investment visible through licence transparency, published audit certificates, granular account controls, and specific technical answers to direct questions. Players who adopt the verification habits outlined here no longer rely on vague reputation or affiliate assurances. They evaluate evidence, ask testable questions, and configure their own defences in parallel with the platform’s measures. The result is a relationship with the gaming environment built on documented protection rather than hopeful assumption, which is exactly what the title’s fresh look at security measures calls for.
OTHER NEWS
Rainbet Casino: Quick Sessions, Big Swings, and the Art of the Fast Spin
Genuine Chances and Unlimited Entertainment with Bbet Casino for UK Players
CrownPlay Kaszinó: Szabad Pörgetések és Jackpotok Otthona Magyarországon
CrownPlay Kaszinó: Szabad Pörgetések és Jackpotok Otthona Magyarországon
Play Smarter Win Confidently in UK with Blaze Spins Casino
GoldBet free spins zonder storting – betaalmethoden & snelle opname
GoldBet no deposit promo code – Hoe je account verifieert en de bonus claimt
GoldBet casino no deposit bonus – beveiligingsgids voor Nederlandse spelers
GoldBet no deposit bonus codes in Nederland: volledige gids
GoldBet promo codes 2026 – volledige review en gids voor Nederlandse spelers
SPECIAL OFFERS
ENHANCED CRUISE WITH CONFIDENCE POLICY
Learn more about how our special offers make your even more offers.
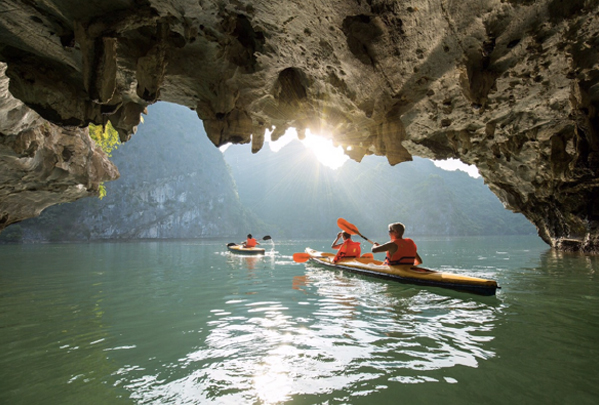
Itinerary 2D/1N – All inclusive
Journey: Hanoi – Halong Bay - Lan Ha Bay - Hanoi
Sightseeing: Dark & Bright Cave - Tra Bau Floating Village
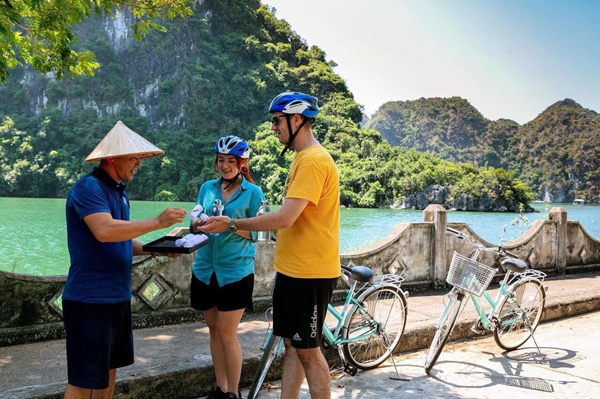
Itinerary 3D/2N – All inclusive
Journey: Hanoi – Halong Bay - Lan Ha Bay - Hanoi.
Sightseeing: Dark & Bright Cave - Tra Bau Floating Village – Viet Hai Village – Three Peaches Beach.
Itinerary 1 Day/6 Hrs – All inclusive
Journey: Hanoi – Halong Bay - Hanoi.
Sightseeing: Surprising Cave – Titop Island – Luon Cave.